
Security& Data
What’s Included:
- Vulnerability assessments
- Penetration testing
- Access & secrets management
- Compliance readiness
We make security a property of the system — enforced by the code and the pipeline — rather than a checklist somebody runs the week before launch.
Working Process
- Threat Model First – Who would attack this, what for, and what it would cost you. Controls are chosen against that, not against a generic list.
- Test, Then Fix – Assessment and penetration testing with findings ranked by real exploitability, then remediation work alongside your team rather than a report handed over.
- Keep It Enforced – Dependency scanning, secrets detection and access reviews wired into the pipeline, plus 6–12 months of support.
Controls That Survive The Next Deploy
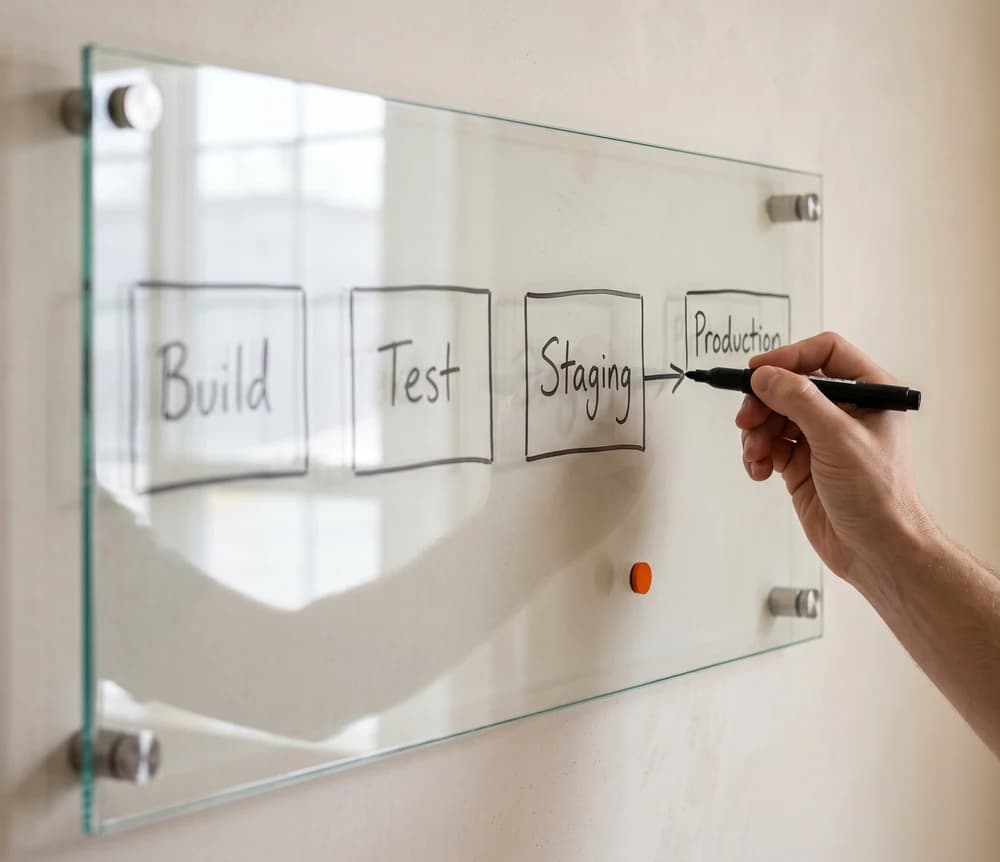
A fix that depends on a person remembering is not a fix. Every control we put in place is enforced by the pipeline, so it holds after the engagement ends.
- Whether you are preparing for an audit or responding to something that already went wrong, the work starts with an honest inventory of data, access and exposure.
- We cover every stage — threat modelling, authentication and authorisation design, encryption, compliance evidence, monitoring and incident response planning.
What We Deliver
- Vulnerability assessments and penetration testing
- Access control, authentication and secrets management
- Compliance support (GDPR, PCI-DSS, SOC 2 readiness)
- Security monitoring and incident response planning
Evidence Your Auditor Will Accept
Findings, remediation history and policy documents are written for the people who will ask for them later — auditors, enterprise buyers and your own board.
Tools & Tech
- OWASP
- Snyk
- Vault
- Cloudflare
Platforms, storefronts and internal systems delivered for clients across eCommerce, health tech, fintech and logistics.
Client satisfaction across delivered engagements — measured on what shipped, not on what was promised at kickoff.
Typical uptime after migration, with monitoring, alerting and zero-downtime deploys set up as part of the build.
What You Get
One senior team from discovery through to launch and beyond — weekly written updates, an open backlog, and direct access to the engineers doing the work. The people in your kickoff call are the people writing the code.
- Assessment – Findings ranked by exploitability and business impact, not by scanner severity alone.
- Remediation – Fixes implemented with your team, and controls enforced in CI so they cannot silently regress.
- Handover & support – Policies, evidence and monitoring you own, plus 6–12 months of post-launch support.
[ Project Brief ]
Bring us the brief, webring back the scope
Tell us what the system has to do, the metric you'd move, andthe deadline. Within 4 business hours we send back a writtenscope, a fixed estimate, and the two projects closest to theproblem you're describing.
Rather say it than type it?
Both of these reach the engineers who would do the work — no account manager in between, no discovery deck before the first question.
- eCommerce & Retail
- Health Tech
- Manufacturing
- Logistics
- Hospitality
- Education
- Fintech
- Real Estate
- SaaS & B2B
The engineers who will actually build your system
[ OUR TEAM ]
